AI Is Changing Network Security. Tufin Is Leading the Way.
Learn More


VMware NSX Reference Design Document
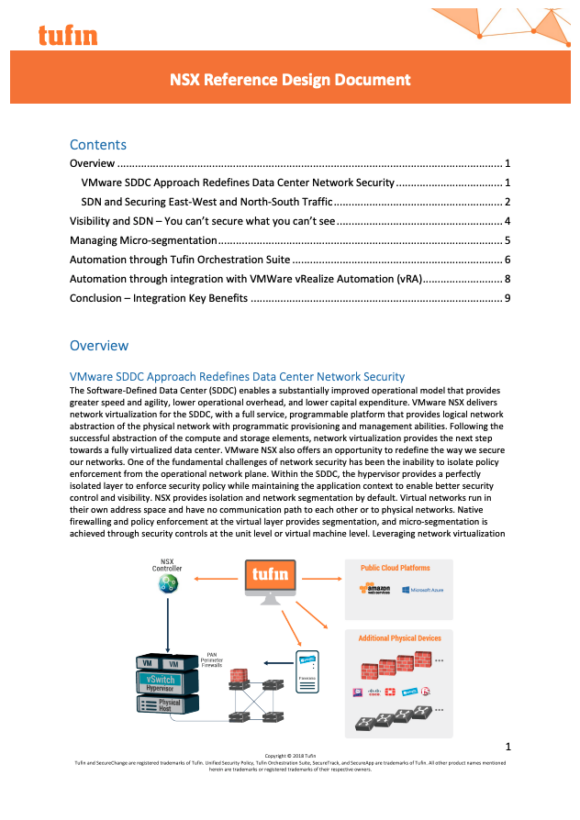
A technical reference design for integrating Tufin with VMware NSX, delivering unified policy visibility, managed micro-segmentation, and policy-driven change automation across physical, virtual, and hybrid cloud environments.
VMware NSX redefines data center network security by moving enforcement into the hypervisor and making micro-segmentation operationally feasible. But most enterprise networks are hybrid: NSX environments sit alongside legacy firewalls, next-generation firewalls, and cloud platforms, each enforcing its own policies. Securing both east-west traffic inside the NSX environment and north-south traffic between NSX and the rest of the data center requires unified visibility and policy management that no single vendor’s console delivers alone.
Download the reference design to see how Tufin integrates with VMware NSX across four key use cases: visibility across NSX and multi-vendor firewalls (Check Point, Palo Alto, Cisco, Fortinet), defining and managing micro-segmentation inside and beyond the NSX environment, policy-driven change automation through Tufin SecureChange with built-in risk analysis, and integrated change automation through VMware vRealize Orchestrator (vRO). The document covers architecture, use cases, APIs, and integration workflows for technical teams.
Get Started with Tufin
Contact our experts to learn more about pricing, receive a free network and firewall risk assessment, or schedule a demo.