AI Is Changing Network Security. Tufin Is Leading the Way.
Learn More


Reduce Firewall Rule Permissiveness Automatically – with Automatic Policy Generator
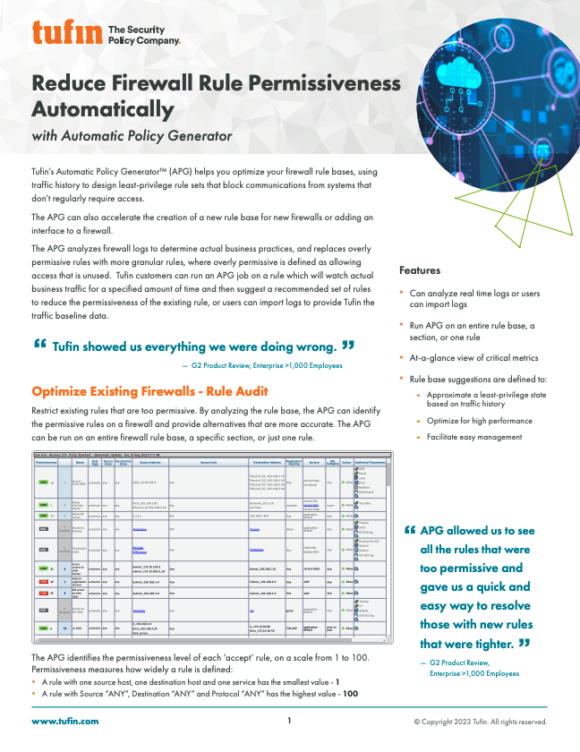
Replace overly permissive firewall rules with least-privilege alternatives, based on actual traffic history. Automatic Policy Generator analyses firewall logs to see what access is really used, and recommends tighter rule sets that reduce attack surface without breaking the business.
Every firewall rule base accumulates “Any Any Allow” permissiveness over time. Rules get written for specific projects, scoped broadly to avoid breaking things, and then never tightened once the real traffic pattern is clear. The result is a growing attack surface, an audit finding waiting to happen, and policies that enforce far more access than the business actually needs. Tightening rules manually requires analysing logs across every firewall, correlating actual traffic with each rule, and designing more granular replacements. For large rule bases, this is practically impossible by hand.
Download the solution brief to see how Tufin’s Automatic Policy Generator analyses firewall logs to identify actual business traffic patterns and recommends more granular rule sets that reduce permissiveness without blocking legitimate access. Run APG on an entire rule base, a specific section, or a single rule. Measure each rule’s permissiveness level on a scale from 1 to 100. Replace broad rules with specific source, destination, and service combinations based on what traffic actually traverses the firewall. Use APG to tighten legacy rule bases or to design optimized rules for brand new firewalls based on an initial permissive policy.
Get Started with Tufin
Contact our experts to learn more about pricing, receive a free network and firewall risk assessment, or schedule a demo.