AI Is Changing Network Security. Tufin Is Leading the Way.
Learn More


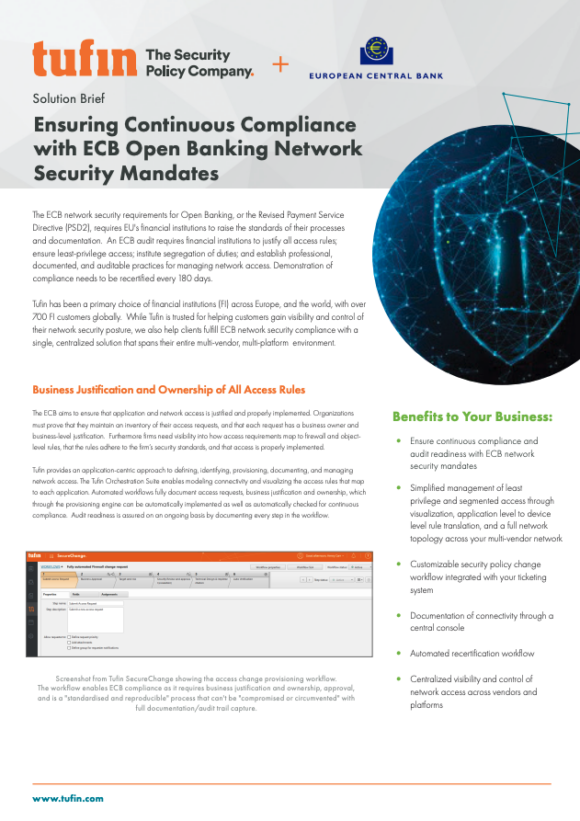
Ensuring Continuous Compliance with ECB Open Banking Network Security Mandates
Operationalize European Central Bank network security requirements for Open Banking and PSD2 across your multi-vendor environment, from application-centric access justification to least-privilege segmentation, segregation of duties, and tamper-proof recertification every 180 days.
European financial institutions subject to ECB oversight face specific network security obligations under the Revised Payment Service Directive (PSD2) and ECB Open Banking requirements. Every access rule must be justified. Least-privilege access must be demonstrated. Segregation of duties must be enforced. Access must be recertified every 180 days with tamper-proof audit trails. Firms that cannot demonstrate compliance face heavy penalties, including the requirement to shut down non-compliant applications until remediation is complete.
Download the solution brief to see how Tufin helps European financial institutions achieve and maintain continuous ECB compliance across multi-vendor hybrid networks. Document business justification and ownership for every access rule, enforce least-privilege access and zone-to-zone segmentation, apply role-based access control for segregation of duties across request, approval, design, and provisioning, run automated 180-day recertification workflows with full audit trails, and demonstrate compliance to auditors at the push of a button, all from a single centralized solution.
Get Started with Tufin
Contact our experts to learn more about pricing, receive a free network and firewall risk assessment, or schedule a demo.