
AI Is Changing Network Security. Tufin Is Leading the Way.
Learn More


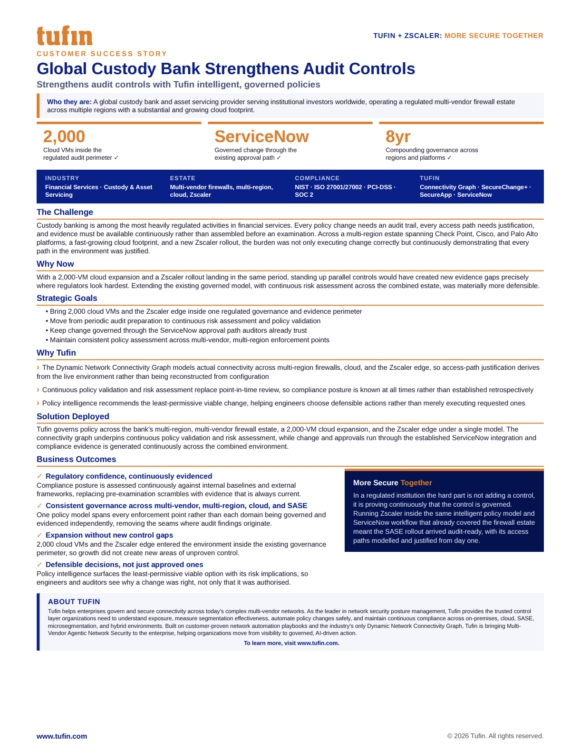
Global Custody Bank Strengthens Audit Controls with Tufin
Download the case study to see how a global custody bank brought 2,000 cloud VMs and its Zscaler rollout inside a single governed audit perimeter — moving from periodic audit prep to continuous, evidenced compliance across a multi-vendor, multi-region estate.
The Challenge: Proving Every Access Path in One of Financial Services’ Most Regulated Environments
- Continuous Evidence, Not Point-in-Time: Every policy change needed an audit trail and every access path needed justification — with evidence available continuously, not assembled before an examination.
- Parallel Rollouts, Parallel Risk: A 2,000-VM cloud expansion and a new Zscaler rollout landing in the same period risked creating new evidence gaps precisely where regulators look hardest.
- Multi-Vendor, Multi-Region Complexity: Governing change consistently across Check Point, Cisco, and Palo Alto platforms — plus cloud and SASE — required one model rather than each domain being evidenced independently.
The Results: One Governed Perimeter Across Firewalls, Cloud, and SASE
- 2,000 Cloud VMs and Zscaler Inside One Audit Perimeter: Cloud and SASE expansion entered the environment inside the existing governance model, so growth did not create new areas of unproven control.
- Continuous Regulatory Confidence: Compliance posture continuously evidenced against internal baselines and frameworks (NIST, ISO 27001/27002, PCI-DSS, SOC 2), replacing pre-examination scrambles.
- Defensible Decisions Through Governed Change: Change and approvals run through the established ServiceNow path, with policy intelligence surfacing the least-permissive viable option — so engineers and auditors see why a change was right, not just that it was authorised.
Get Started with Tufin
Contact our experts to learn more about pricing, receive a free network and firewall risk assessment, or schedule a demo.