
AI Is Changing Network Security. Tufin Is Leading the Way.
Learn More


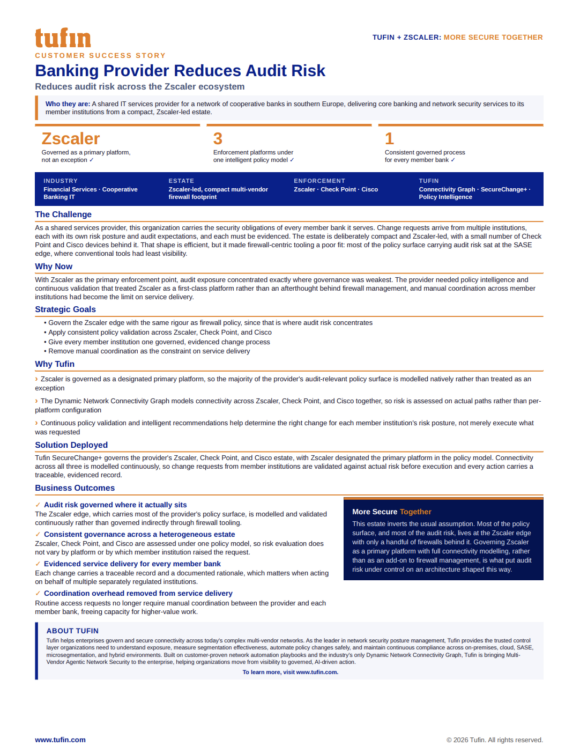
Cooperative Banking Provider Reduces Audit Risk Across the Zscaler Ecosystem with Tufin
Download the case study to see how a shared IT services provider for cooperative banks in southern Europe governs its Zscaler-led estate as a first-class platform — bringing Zscaler, Check Point, and Cisco under one intelligent policy model and one evidenced change process for every member bank.
The Challenge: Audit Risk Concentrated at the SASE Edge, Where Firewall-Centric Tooling Couldn’t See
- Zscaler-Led Estate, Firewall-Centric Tools: Most of the policy surface carrying audit risk sat at the SASE edge, where conventional firewall tooling had the least visibility.
- Shared Obligations Across Many Institutions: As a shared services provider, the organization carried the security obligations of every member bank it served — each with its own risk posture and audit expectations.
- Manual Coordination as the Ceiling: Manual coordination across member institutions had become the limit on service delivery, blocking scale on routine access requests.
The Results: Zscaler Governed as a Primary Platform, Not an Exception
- Audit Risk Governed Where It Actually Sits: The Zscaler edge is modelled and validated continuously as a designated primary platform, rather than governed indirectly through firewall tooling.
- Consistent Governance Across Zscaler, Check Point, and Cisco: One policy model spans all three enforcement platforms, so risk evaluation doesn’t vary by platform or by which member institution raised the request.
- Evidenced Service Delivery for Every Member Bank: Each change carries a traceable record and documented rationale, and manual coordination overhead is removed — freeing capacity for higher-value work.
Get Started with Tufin
Contact our experts to learn more about pricing, receive a free network and firewall risk assessment, or schedule a demo.